Move approvals into an application when email makes it hard to identify the current request, authorized decision-maker, or reason for a decision. A successful migration defines exceptions and record ownership before building screens; otherwise, it merely relocates confusion.
Email is a poor system of record for complex approvals
Moving approvals out of email is useful when teams cannot reliably tell who owns a request, which version was approved, or why an exception was accepted. A custom application can make the request, decision, and history part of one controlled workflow. It is not automatically better: if approvals are rare, simple, and easy to retrieve, a disciplined email process may be enough.
The important question is not whether email is old-fashioned. It is whether the current process preserves the information and accountability your business needs. An application should encode the rules that matter while leaving a clear route for unusual cases.
Diagnose the failures before specifying software
Look for repeated forwarding, approval requests sent to the wrong person, decisions buried in long threads, and uncertainty about whether a change was approved. Also check for duplicate requests, missing attachments, unclear substitutes during leave, and requests that stall without anyone noticing.
Talk to people on both sides of the decision. Ask submitters what makes a request incomplete and approvers what evidence they need. Map a few real examples from submission through final action, including one rejection and one exception. This exposes the actual workflow rather than the version remembered in a policy document.
Define decisions, exceptions, and ownership
For each request type, identify who may approve, reject, return, or escalate it. A role-based permission grants access according to a job or responsibility rather than an individual name; it can help when staff change, but the business still needs an owner for each role and a process for maintaining membership.
Write down what happens when an approver is unavailable, a request changes after review, or a decision conflicts with policy. Decide whether a changed request restarts approval or goes only to affected reviewers. Avoid a vague “manager override”: record who used it, why, and what authority permitted it.
Design the record and state transitions
An approval record should capture the submitted data, submitter identity, relevant attachments or references, current status, decision-maker, timestamp, and comments. Preserve the submitted version that was reviewed. If a request is edited later, retain the prior version or clearly show what changed and whether that change invalidated earlier decisions.
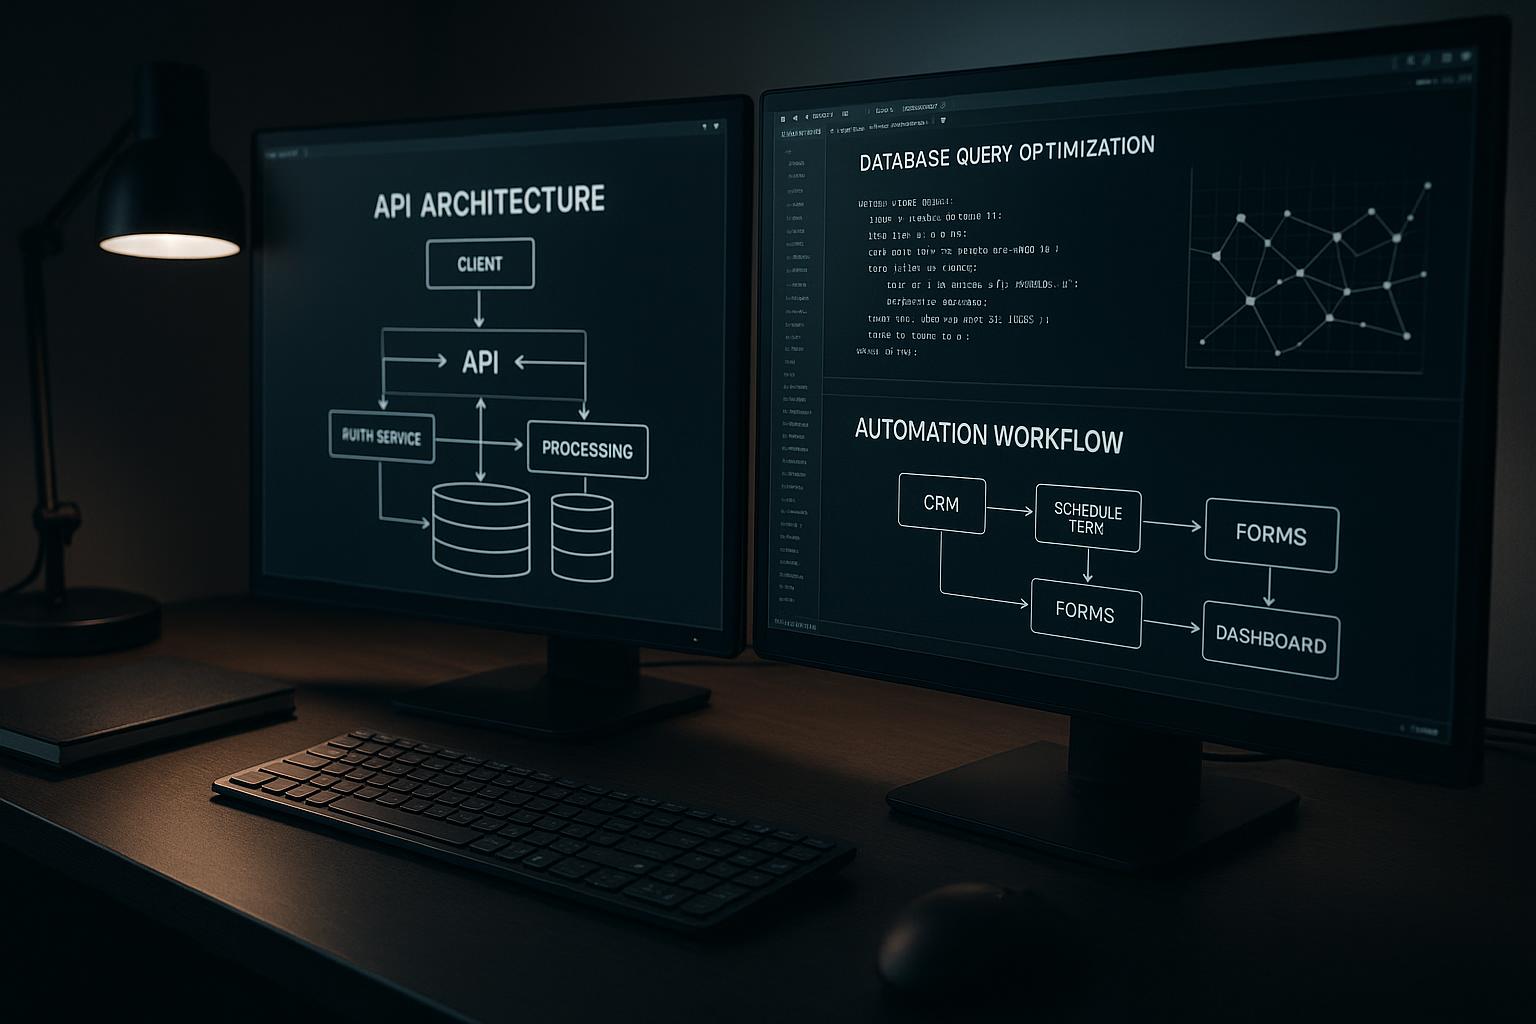
Model the workflow as explicit states, such as draft, submitted, returned, approved, and rejected. Define allowed transitions and validate them on the server, not just in the page interface. This prevents a user from reaching an unauthorized state by bypassing a screen. Decide how long records must remain available and how authorized staff can export them.
Make notifications and failures recoverable
Notifications help people act, but email or text should not become the only record of a decision. The application should show pending work and send reminders based on rules the business can explain. If a notification service fails, the approval itself should remain saved, and an owner should be able to identify and resend the message without creating a duplicate decision.
Define what users see after saving, what happens if a page times out, and how duplicate submissions are handled. A safe design can recognize repeated attempts for the same request rather than silently creating multiple active records. Log meaningful actions and errors, while limiting sensitive details in general-purpose logs.
Pilot the workflow with real exceptions
Start with one approval type that has a clear owner and manageable variation. Configure permissions, statuses, notifications, and record retention; then test ordinary submissions alongside incomplete requests, reassignments, rejections, edits, and outages. Include the staff who will use and administer the process.
A hypothetical example: a facilities team routes equipment purchases for review. A complete request goes to the budget owner; missing documentation returns to the submitter; an urgent exception requires a reason and a named higher-level decision-maker. The team can verify whether each path records the right evidence and whether staff can recover a failed notification. Measure completion time, pending age, returned requests, and audit-record completeness rather than assuming the application improved the process.
A practical workflow migration checklist
- List every approval type, including exceptions, rejections, escalations, and changes after submission.
- Name the person or role allowed to decide at each step, plus a backup for absences.
- Define what information and evidence approvers need, and which records they may access.
- Specify status transitions, deadlines, notifications, and what happens when an action fails.
- Test ordinary and unusual cases with the people who submit, review, and audit requests.
- Set a retention and export policy for decisions, comments, attachments, and identity records.
Questions about this approach
Does every email approval process need a custom application?
Not necessarily. If a shared tool already supports controlled access, version history, clear ownership, and reliable retrieval, it may be sufficient. Consider custom development when the approval rules or connections to existing business data require behavior that your current tools cannot safely provide.
Should email notifications count as the approval record?
Keep the decision and its evidence in the application record, even if the person is notified by email. A notification can link them back to the request, but it should not replace the recorded identity, decision, timestamp, and any required explanation.
What should we verify before launching the workflow?
Test a deliberate set of cases: a normal approval, a rejection, an incomplete request, a reassignment, an edit after review, a duplicate submission, and a notification or access failure. Confirm that permissions, status, history, and recovery behavior match the written rules.
For help applying this approach, explore our custom programming services.
Discuss your project with Full Blown Studio
Tell us what needs to work better and what you have tried. Discuss your project, email bob@fullblown.com, or call (661) 429-0940.